Most AI governance advice assumes you have a governance committee, a model risk function, and a data science team to answer to it. If you are a 150-person company in Texas running Microsoft 365 and Copilot, none of that describes you — and the advice built for it does not travel down.
What a mid-market business actually needs is simpler: an honest read on where it stands, and the one thing to fix next. That is what a maturity model gives you.
There is also a deadline attached now. The Texas Responsible Artificial Intelligence Governance Act took effect January 1, 2026, and it applies by business activity rather than headcount — a 30-person company serving Texas customers is inside its scope. The law offers safe harbor to organizations that substantially comply with the NIST AI Risk Management Framework. Levels 4 and 5 below are what that safe harbor actually requires. Levels 1 through 3 do not get you there.
What an AI governance maturity model is
An AI governance maturity model is a scale that tells you how much control your business actually has over the AI it uses. Level 1 is no control. Level 5 is control you can prove.

It answers one question: where are we right now? Not where should we be — everyone already knows that answer. The honest read on today is what tells you what to fix next.
Most companies guess a level too high. A written policy feels like control, so a business that has one assumes it is well along. But if nothing stops an employee from breaking that policy, the policy is a statement of intent. That business is at level 2, not level 3.
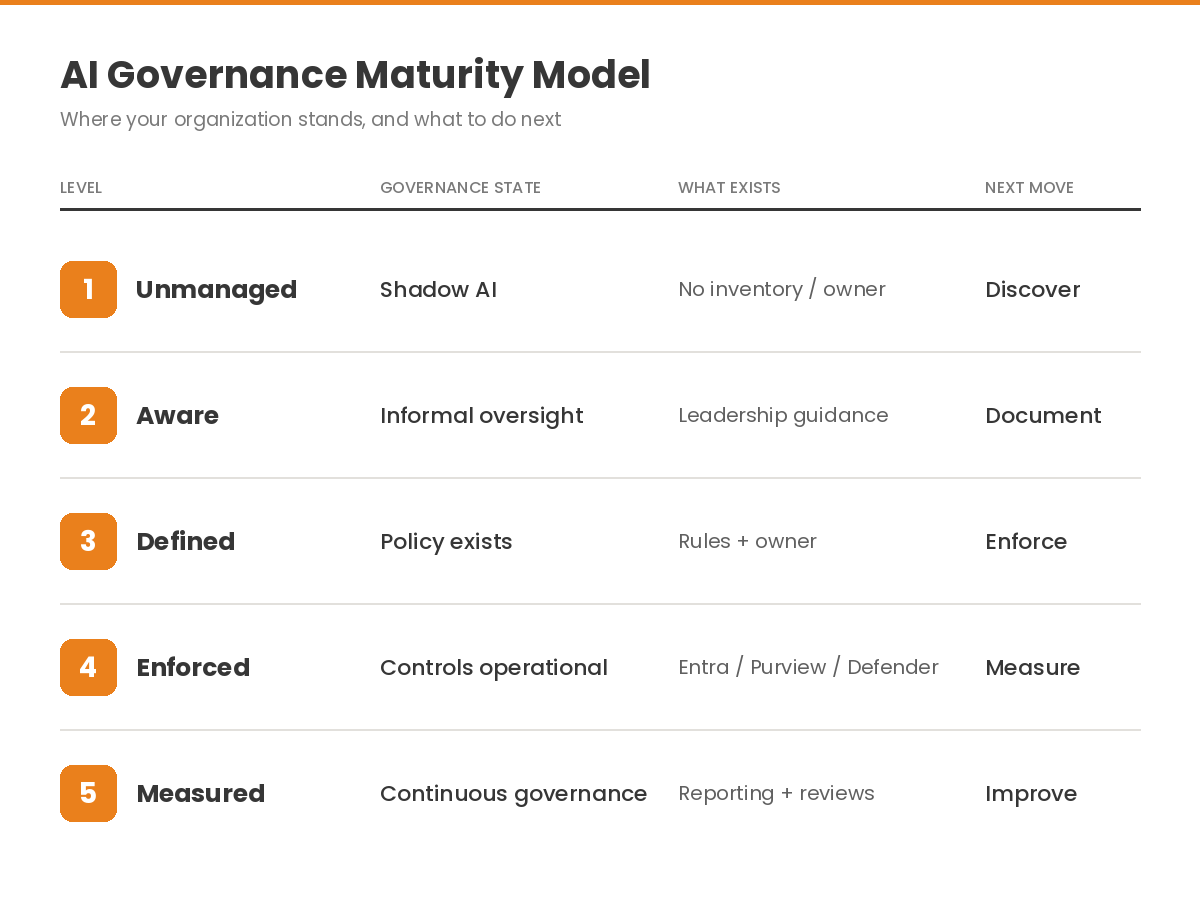
The 5 levels
Level 1 — Unmanaged
AI is in daily use and nobody owns it. Employees have brought in tools on their own initiative, most of them through personal accounts, and no one at the company could produce a list of what is being used or what data has passed through it. This is shadow AI, and it is the default state for any business that has not deliberately moved off it.
The exposure is not hypothetical at this level. Client data, financial records, and credentials go into consumer tools that retain and train on input, and the company has no record that it happened. Under TRAIGA’s 60-day cure period, you cannot cure what you cannot see.

Move up by finding out what is actually in use. Ask the team directly, then check what is authenticating against your Microsoft 365 tenant. The answer is usually larger than leadership expects.
Producing that list is the point of a readiness assessment, and it is where we start with most clients. The first deliverable is the inventory nobody in the business could produce on their own.
Level 2 — Aware
Leadership knows AI is being used and has said something about it — a message in Teams, a line in an all-hands, maybe a paragraph added to the handbook. Nothing is enforced and nobody owns the outcome.
This is the most common place for a mid-market company to sit, and the most misleading, because it feels like progress. It is not. An informal expectation produces inconsistent behavior across departments and gives you nothing to show a regulator or an insurer, and it does nothing to pull shadow AI back into view.

Most businesses we assess are sitting at level 1 or 2 when we first engage. That is what an initial AI readiness engagement is built to address.
Move up by writing the rules down and naming an owner. The document does not need to be long. It needs to name approved tools, prohibited data, and a person.
Level 3 — Defined
A written acceptable use policy exists. Approved tools are listed, data handling rules are explicit, employees have acknowledged it, and someone is accountable for keeping it current. An AI governance policy at this stage does not need to be elaborate — it needs to be specific and owned. If you want the individual items to check off, that is what the AI governance checklist covers.
Level 3 is a real achievement and most companies stall here. The reason is that the next step costs engineering time rather than writing time, and the policy already feels like the finish line.

The weakness is that nothing verifies compliance. You will discover a violation when someone reports it or when it surfaces in an incident, which means late. Move up by making the technical environment match the written rule.
Moving from a written policy to enforced controls is project work, not a document revision. It usually lands as a professional services engagement or part of onboarding — configuring what the policy already says, inside the tenant that already exists.
Level 4 — Enforced
The controls match the policy. Approved AI tools authenticate through your identity provider, so access can be granted and revoked centrally. Data loss prevention rules watch for the data categories the policy prohibits. Sensitivity labels travel with the documents that matter most.
In a Microsoft environment this is mostly configuration rather than procurement — Purview for DLP and labeling, Entra for conditional access and app governance, and Defender for the alerting. Businesses at level 3 frequently already own the licensing for this and have not turned it on. Your Microsoft Secure Score is the fastest way to see how much of it is already active.

Level 4 is where governance stops depending on whether people remember the rule. Move up by adding measurement.
Level 5 — Measured
Someone reviews what the controls are catching. AI use is reported on a cadence, the approved tool list gets revisited quarterly, policy exceptions are logged with a reason, and incidents feed back into the rules.
This is also the level where the TRAIGA safe harbor becomes something you can actually demonstrate. Substantial compliance with the NIST AI Risk Management Framework is a claim you support with records — what you govern, what you found, what you changed. A company at level 5 can produce that file. A company at level 3 can produce a PDF.

Level 5 is not a finish line either. It is the level at which the model starts maintaining itself, because measurement keeps surfacing the next gap.
Sustaining that in-house is difficult, because the measurement has to be continuous and someone has to act on what it returns. That is the shape of an ongoing managed AI service: monitoring that runs 24×7 rather than at review time, reporting monthly and on demand, and training and enablement running alongside — both to reinforce acceptable use and to surface where AI is genuinely worth applying. In a period of constant disruption, the most valuable part is often the guidance itself. An AI steering committee as a service.
How to place your business
Four questions, answered honestly, put you within one level. A full AI maturity assessment goes deeper than this, but these are enough to know where to start:
- Could you produce a current list of every AI tool in use across the company, including shadow AI running on personal accounts? No means level 1.
- Is there a written AI policy with a named owner and a review date? No means level 2.
- Would a technical control stop an employee pasting client data into an unapproved tool right now? No means level 3.
- Has anyone reviewed what those controls caught in the last quarter? No means level 4.
Answering yes to all four puts you at level 5. Most mid-market companies answer no to the first or second, which is a more useful thing to know than any benchmark against a peer average.
How this maps to NIST
The NIST AI Risk Management Framework organizes into four functions — Govern, Map, Measure, and Manage. The maturity levels are not a competing framework; they are a sequence for getting there.
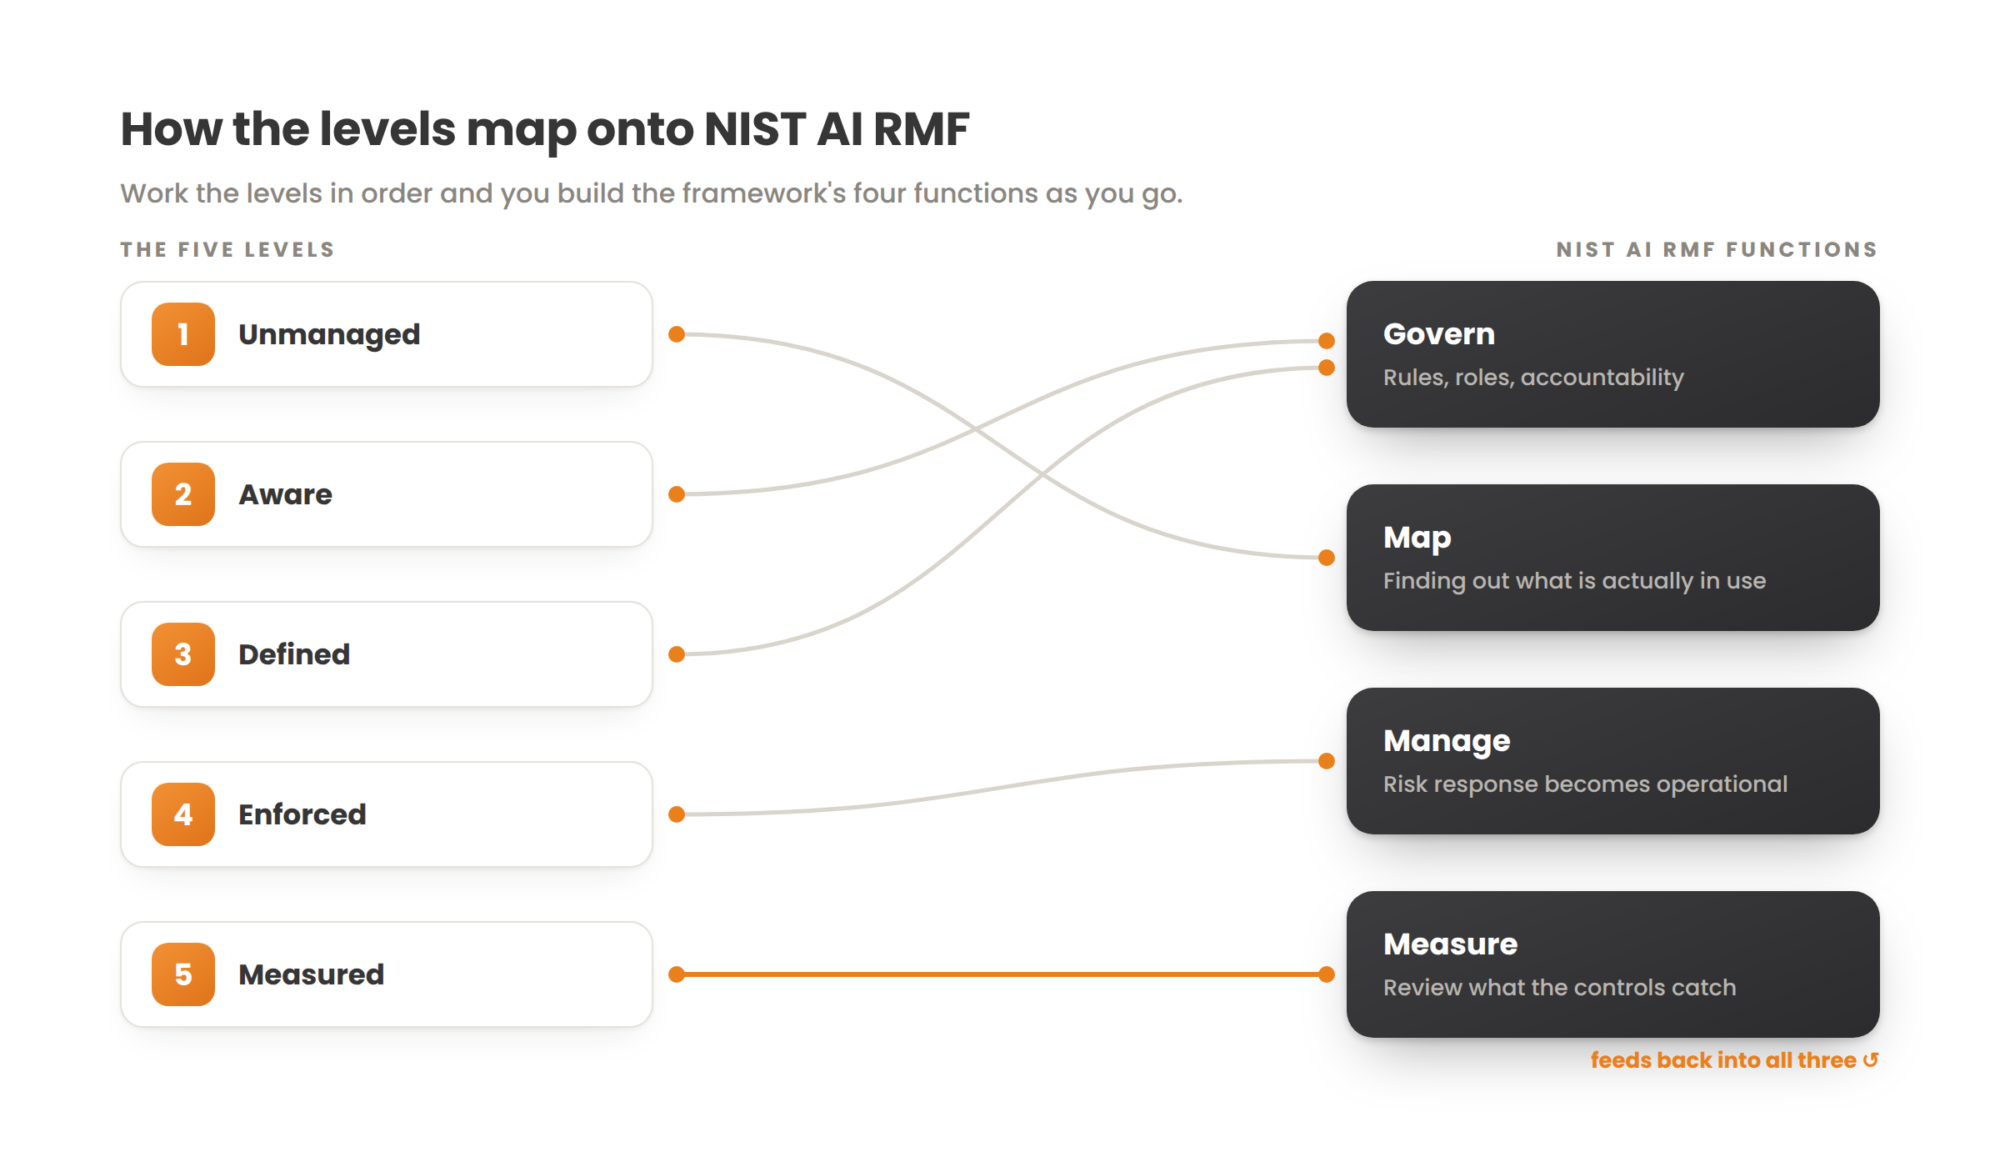
Levels 2 and 3 build Govern: rules, roles, accountability. Level 1 to 2 is Map, in that finding out what is in use is the mapping exercise. Level 4 is Manage, where risk response becomes operational. Level 5 is Measure, and it feeds back into all three.
It also runs alongside the data governance you already have. AI governance is not a separate discipline bolted on — approved tools, classified data, and controlled access are the same controls applied to a new category of software. If you already have an AI adoption framework on paper, the maturity levels tell you whether it is operating or just written down.
The practical consequence is that an SMB can work the levels in order without reading the framework end to end, and still end up substantially aligned with it. That alignment is what the Texas safe harbor is written against.
Why most companies overestimate their level
Two patterns account for nearly all of it.
The first is mistaking a document for a control. A signed policy proves someone read a page. It does not prevent the behavior the page prohibits, and only one of those things helps during an incident.
The second is counting licensing as capability. Owning Microsoft 365 E5 does not mean Purview DLP is configured for AI tools, and the gap between owning the license and having the policy running is where most level 3 companies actually sit. Checking is a short exercise. It is also the one that most often changes leadership’s answer about where the business stands.
Where to start
Find your level before planning anything. The gap between where a business thinks it sits and where it actually sits is usually one full level, and planning against the wrong starting point wastes the quarter.
If you land at level 3 — policy written, nothing enforcing it — the next move is checking what your existing Microsoft licensing already covers. That single step closes more exposure than any additional document will.
If you are not sure which level describes your business, an AI readiness assessment is where that conversation usually starts.
The businesses that get AI governance right are not the ones with the thickest policy binder. They are the ones who know their level and fix the next thing. GCS helps Austin-area businesses work up these levels on the Microsoft stack — from the first AI inventory to enforced controls and ongoing measurement. Talk to our team about where your business stands.
FAQ: AI Governance Maturity Model
Is there an AI maturity model?
There are several, and they differ mainly in audience. IEEE and academic models are built for organizations that develop AI systems. Vendor models tend to track adoption of that vendor’s platform. The five levels above are written for businesses that buy and use AI rather than build it, which is where most mid-market companies sit.
What are the 5 levels of an AI governance maturity model?
Unmanaged, Aware, Defined, Enforced, and Measured. Unmanaged means AI is in use with no oversight. Aware means leadership knows but nothing is written. Defined means a written policy with an owner. Enforced means technical controls match the policy. Measured means someone reviews what those controls catch and acts on it.
What is the difference between an AI governance framework and a maturity model?
A framework describes what good governance contains. A maturity model describes the order you build it in and how far along you are. NIST AI RMF is the framework; the levels are the path through it. Responsible AI sits above both — the principles, like fairness and transparency, that a framework turns into requirements. Most AI governance best practices lists are really level 3 and 4 items with no sequence attached.
What is an AI governance maturity framework and what are its key principles?
A maturity framework combines two things: the principles governance rests on — accountability, transparency, data control, human oversight — and a sequence for putting them in place. The principles tell you what a mature program contains. The levels tell you what to build first. Most businesses fail on sequence rather than principle. They write the accountability statement before they can list the AI tools in use, and the statement ends up describing a company that does not exist yet.
How long does it take to move up a level?
Level 1 to 2 is a conversation. Level 2 to 3 is a document, usually a week or two of drafting and review. Level 3 to 4 is the real work — configuration, testing, and rollout, typically measured in weeks depending on how much of the Microsoft stack is already licensed. Level 4 to 5 is a recurring meeting and a report, which is easy to schedule and easy to let lapse.
Does TRAIGA require an AI governance maturity model?
No. The Texas Responsible Artificial Intelligence Governance Act does not require a maturity model, and no law does. What it offers is safe harbor for organizations that substantially comply with the NIST AI Risk Management Framework or a comparable standard. A maturity model is a way to get there and to show your work — records of what you govern, what you found, and what you changed. The law cares about the substance, not the scale you used to track it.
Who can help a Texas business assess its AI governance maturity?
Most mid-market businesses do this with their managed IT provider, since the assessment needs access to your Microsoft 365 tenant to see what is actually running. GCS Technologies is an Austin-based Microsoft partner and works with SMBs at every stage — from writing a first AI use policy through identifying use cases, setting up governance, and securing the environment. The starting point is usually a readiness assessment that establishes your current level before any roadmap gets written.